Offensive Security
A-01Web, API and mobile testing
- Burp Suite
- Metasploit
- Nuclei
- Frida
- ADB
- Kali Linux
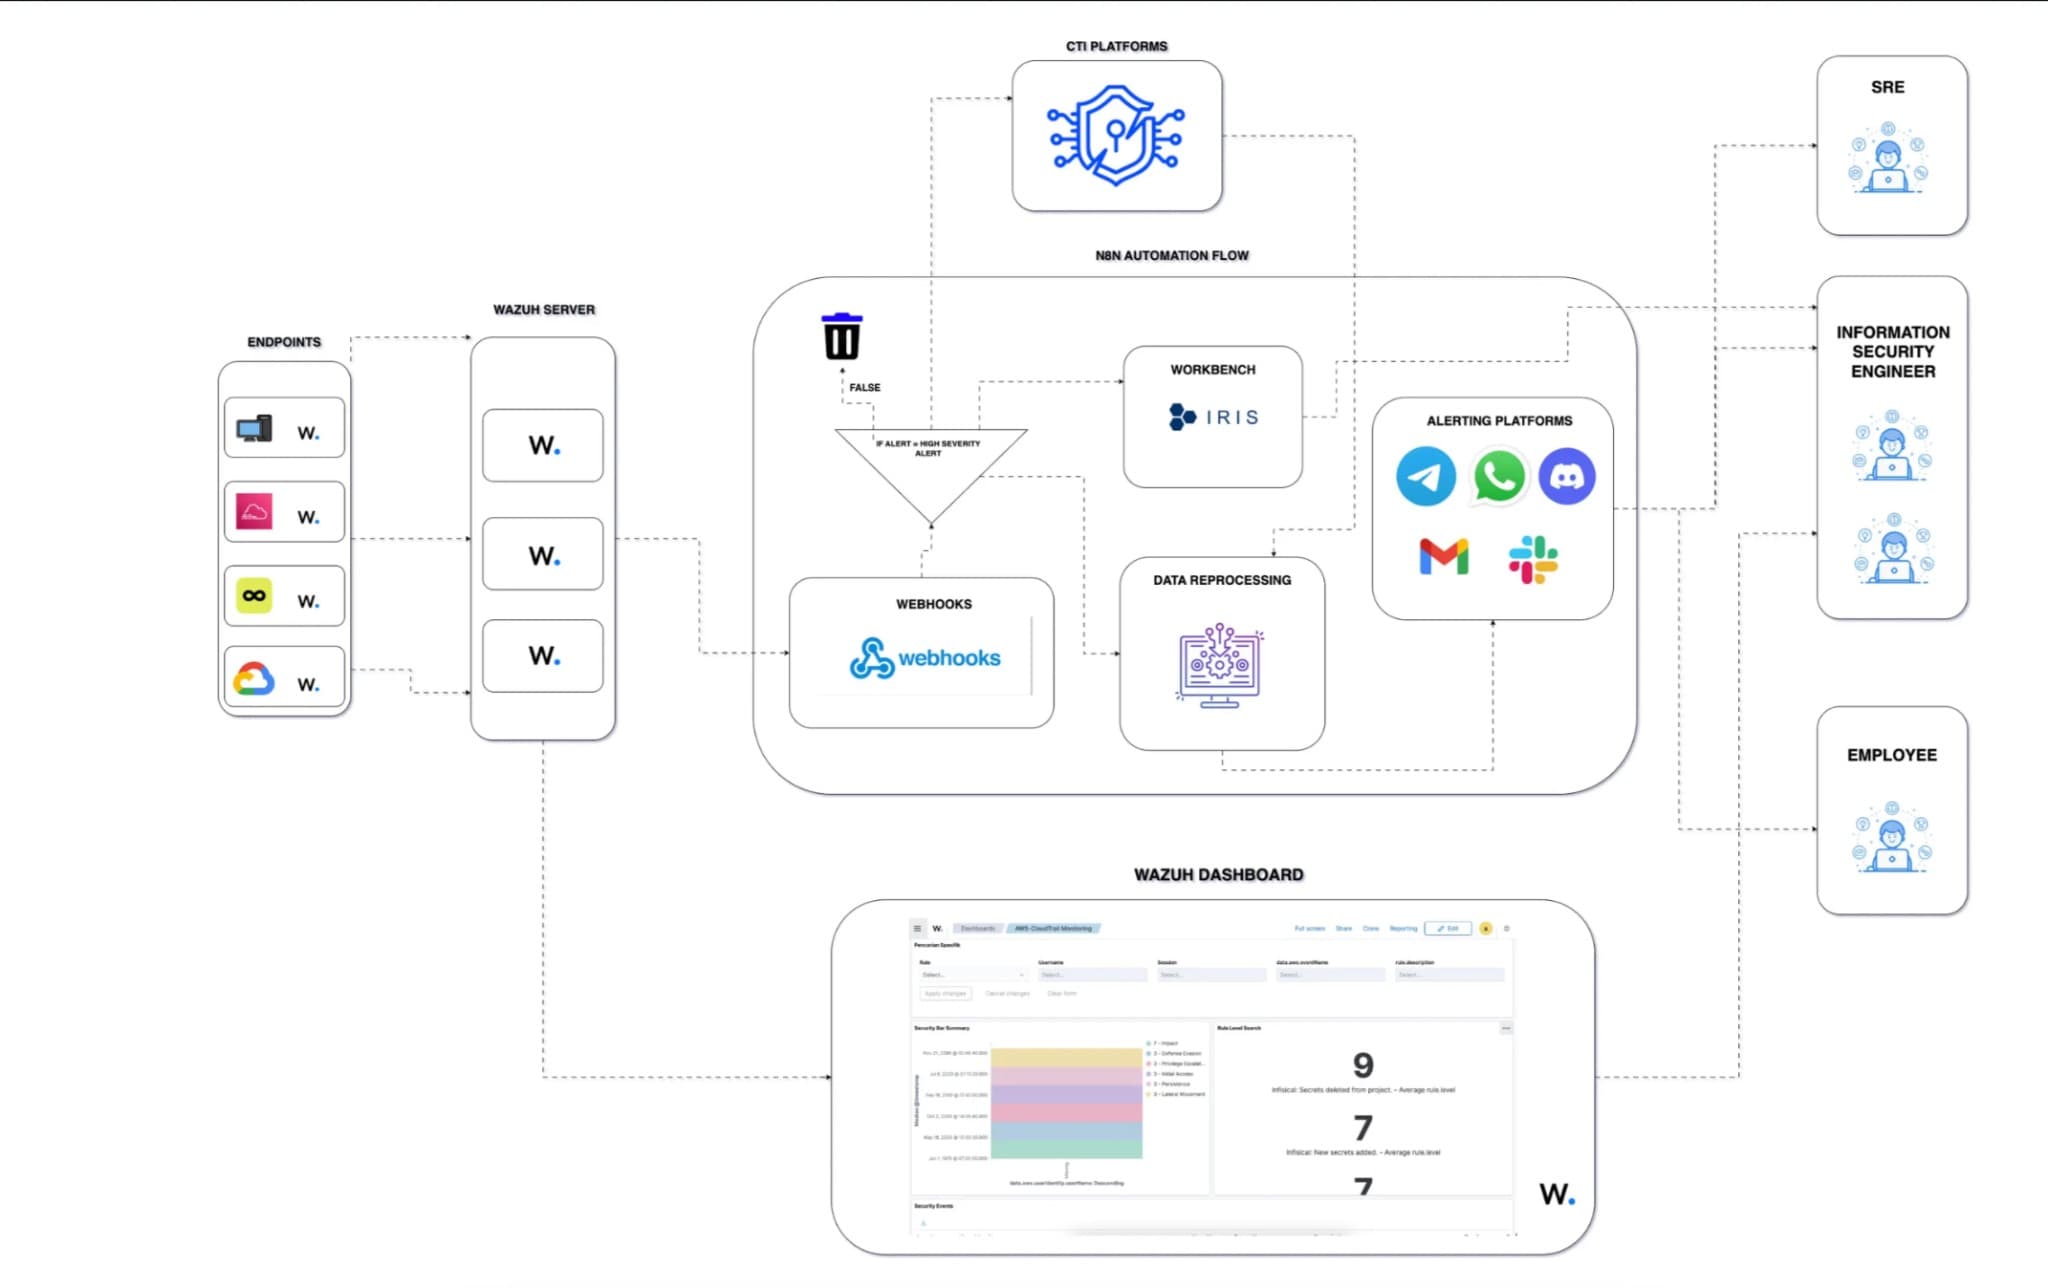
I’m Guntur Wahyu Ramadhan, an Information Security Engineer. I test how systems break, investigate what happened, and turn the findings into detection and automation — from penetration testing to SIEM and SOAR engineering.
$ nmap -sV -p 22,80,8443 lab-target.test
PORT      STATE  SERVICE  VERSION
22/tcp    open   ssh      OpenSSH 8.9
80/tcp    open   http     nginx 1.24
8443/tcp  open   https    Jetty 9.4
1 host up · scan complete
CVE-2021-44228
Apache Log4j2 — JNDI lookup remote code execution (“Log4Shell”)
Illustrative reference · not my disclosure
Chapter 01 · Origin
Now
GdpLabs · Jul 2026 – Present
Detection engineering, SIEM tuning, threat intelligence and hunting.
Previously
Penetration Tester · Widya Security
Web, mobile (Android & iOS) and server penetration testing.
Training
Yogyakarta State University
Information Technology — Bachelor’s Degree
2022 – 2026
Universiti Tun Hussein Onn Malaysia
Online Inbound Mobility: Project Management (Grade: A)
Jul – Sep 2023
Proof of work
Chapter 02 · The strip
Where I spend my time. Each panel links to the real work behind it. The artwork uses fictional lab data.
Chapter 03 · Selected projects
Operations and investigations from my own labs and pipelines. Nothing here is client work.
Chapter 04 · Equipment
Tools I actually use, grouped by the job they do. No skill bars — a tool in the case is not a claim of mastery.
Web, API and mobile testing
Discovery and packet-level investigation
Used across CyberDefenders labs
Detection, SIEM and SOAR
Glue code and tooling
Where the labs live
Frameworks
OWASP ASVS / WSTG · NIST CSF · ISO 27001
Chapter 05 · Field notes
Write-ups and notes, pulled live from my Medium feed.
Final panel · End of issue #01
Have a security project, research idea, or technical challenge worth exploring? Say hello.
To be continued…